Fix · Security operations · Governance
Building Security Readiness Into Operations.
Embedding security requirements into the way the business actually worked.
The problem
The business needed stronger security controls to meet customer expectations, support larger opportunities and prepare for recognised standards. The risk was treating compliance as a collection of policies and evidence created separately from day-to-day operations.
What I did
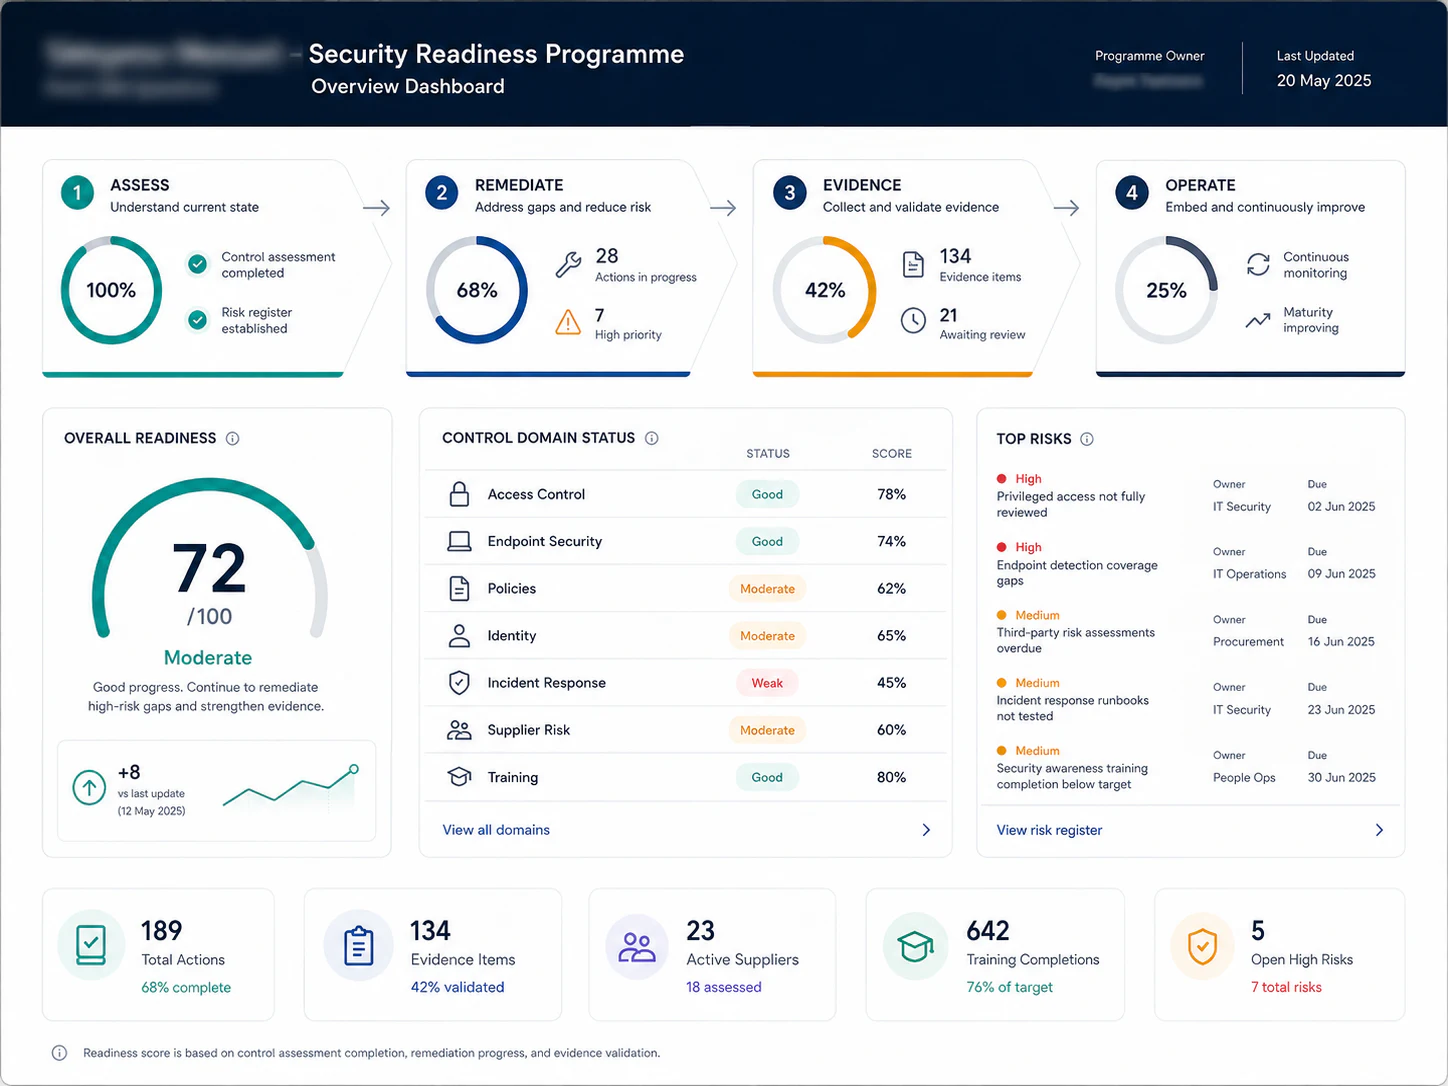
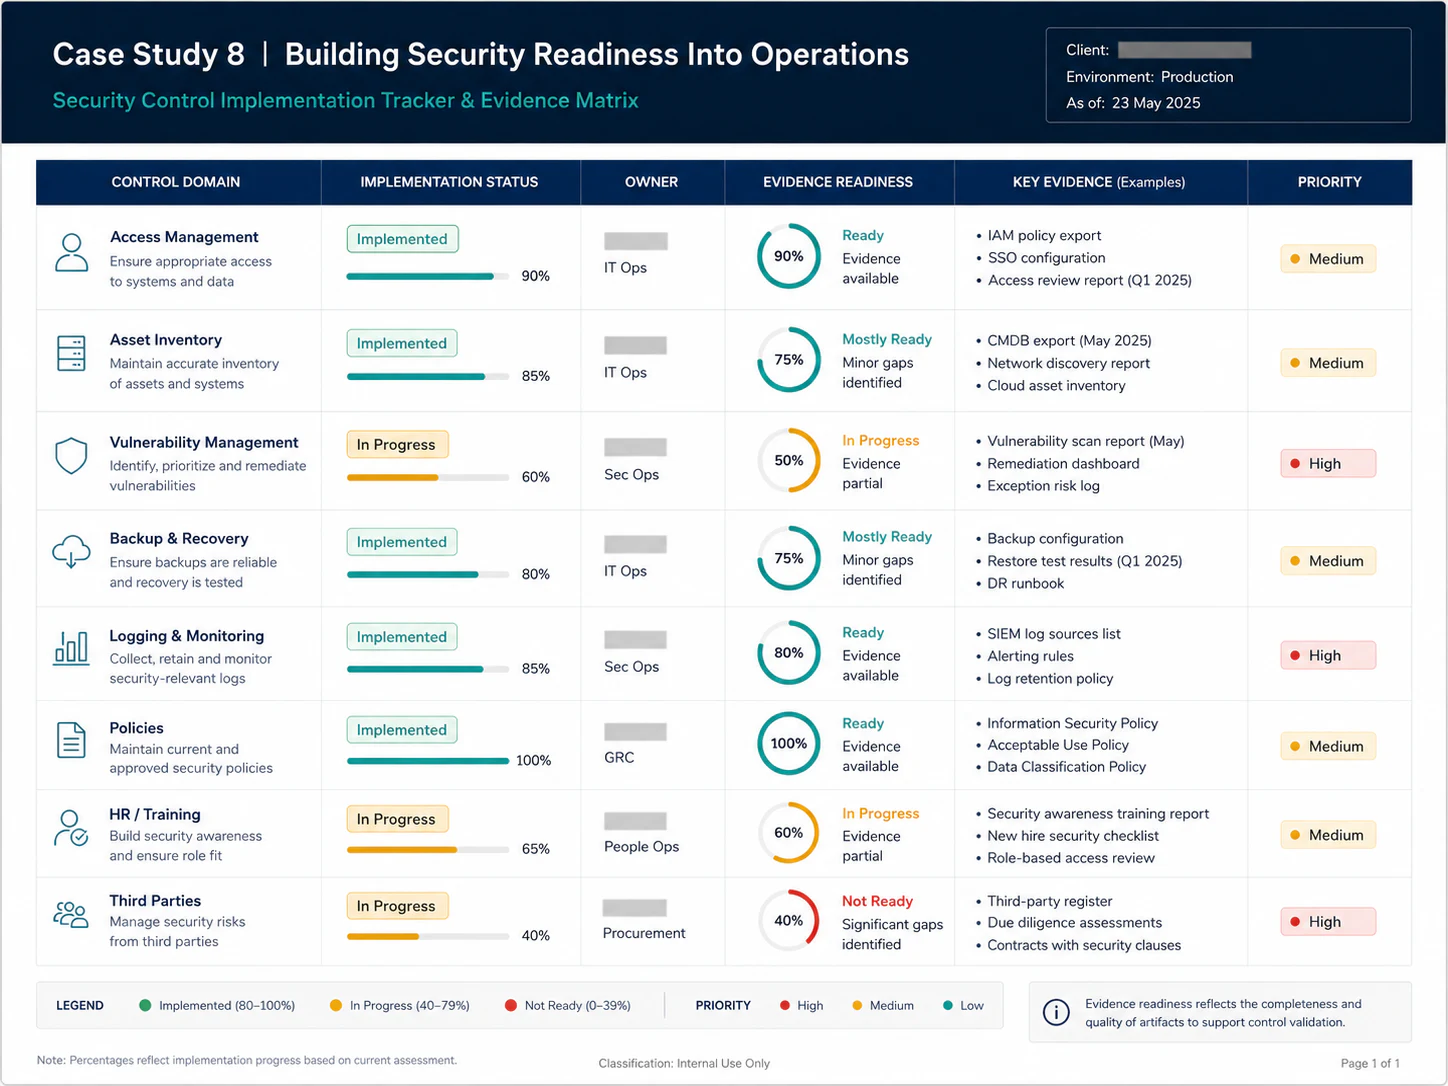
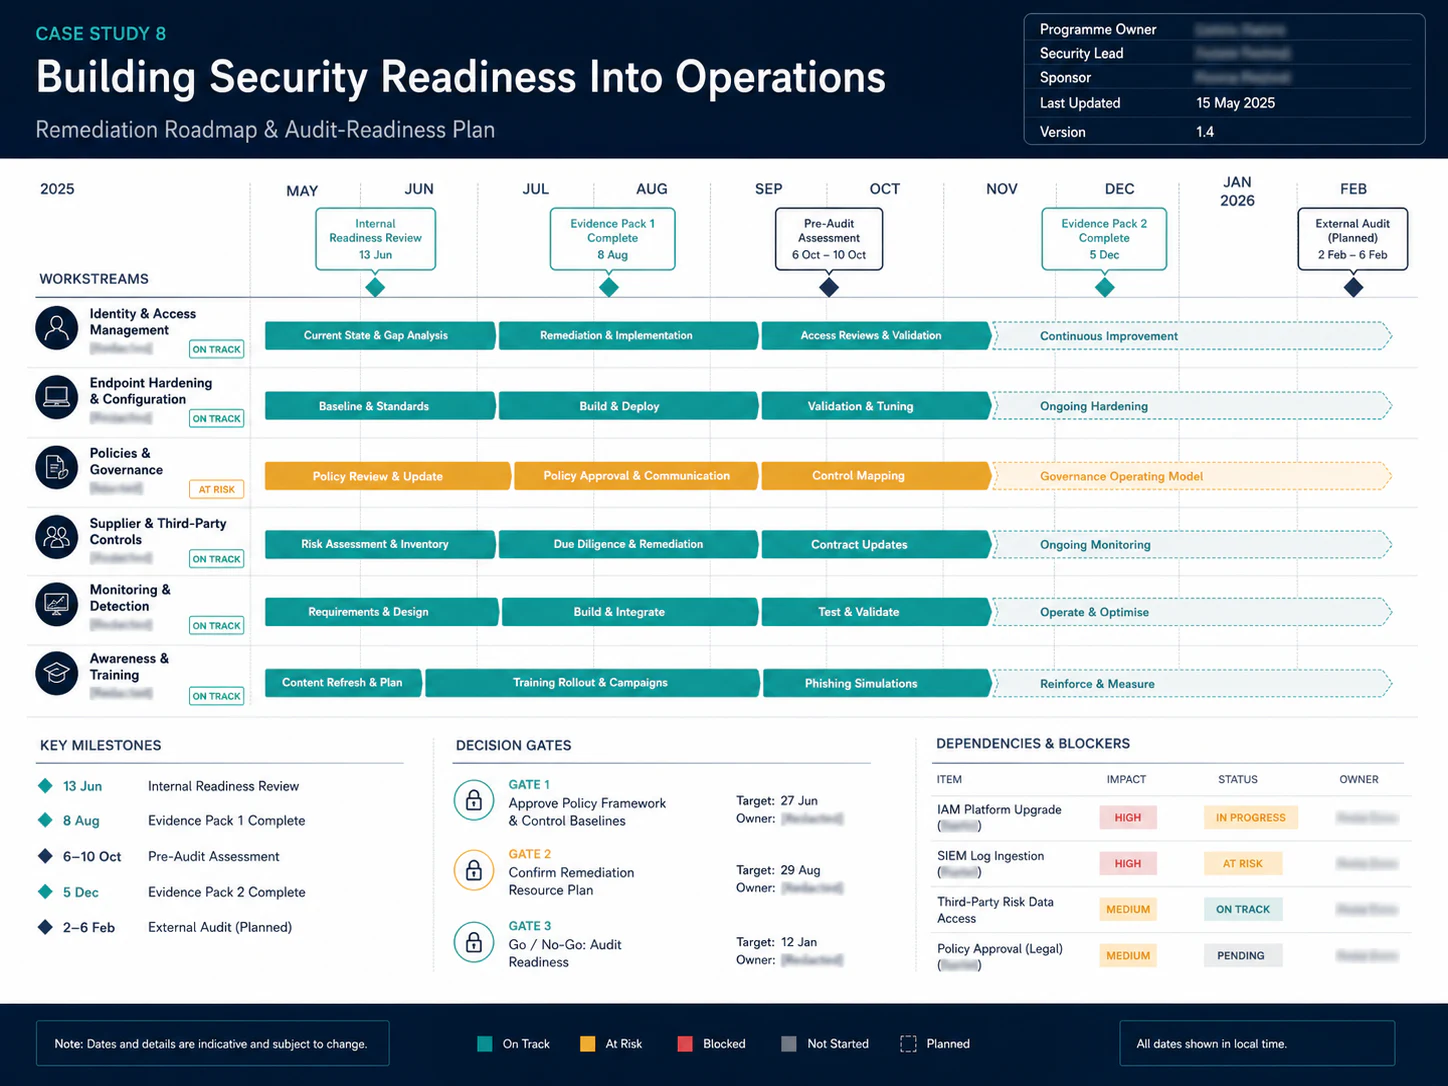
I turned the requirements into an implementation programme. I mapped controls to real owners, systems and processes, identified gaps, prioritised remediation, structured the evidence required, and built the recurring activities needed to keep controls working after the initial assessment. Technical changes, policies, people processes and operational ownership were treated as one programme rather than separate workstreams.
What changed
Security readiness became part of the operating model instead of a last-minute compliance project.
Work involved
Security operations · Cyber Essentials · ISO 27001 readiness · Controls · Governance · Process design · Evidence management
Let’s solve what’s holding you back.
A focused conversation is often the fastest way to get clarity.